October 19, 2026
An AI agent should not inherit everyone’s permissions
A document can carry hostile instructions. When an agent also has broad access, a misleading answer can become a data leak or an unwanted action. Put authorization outside the model.
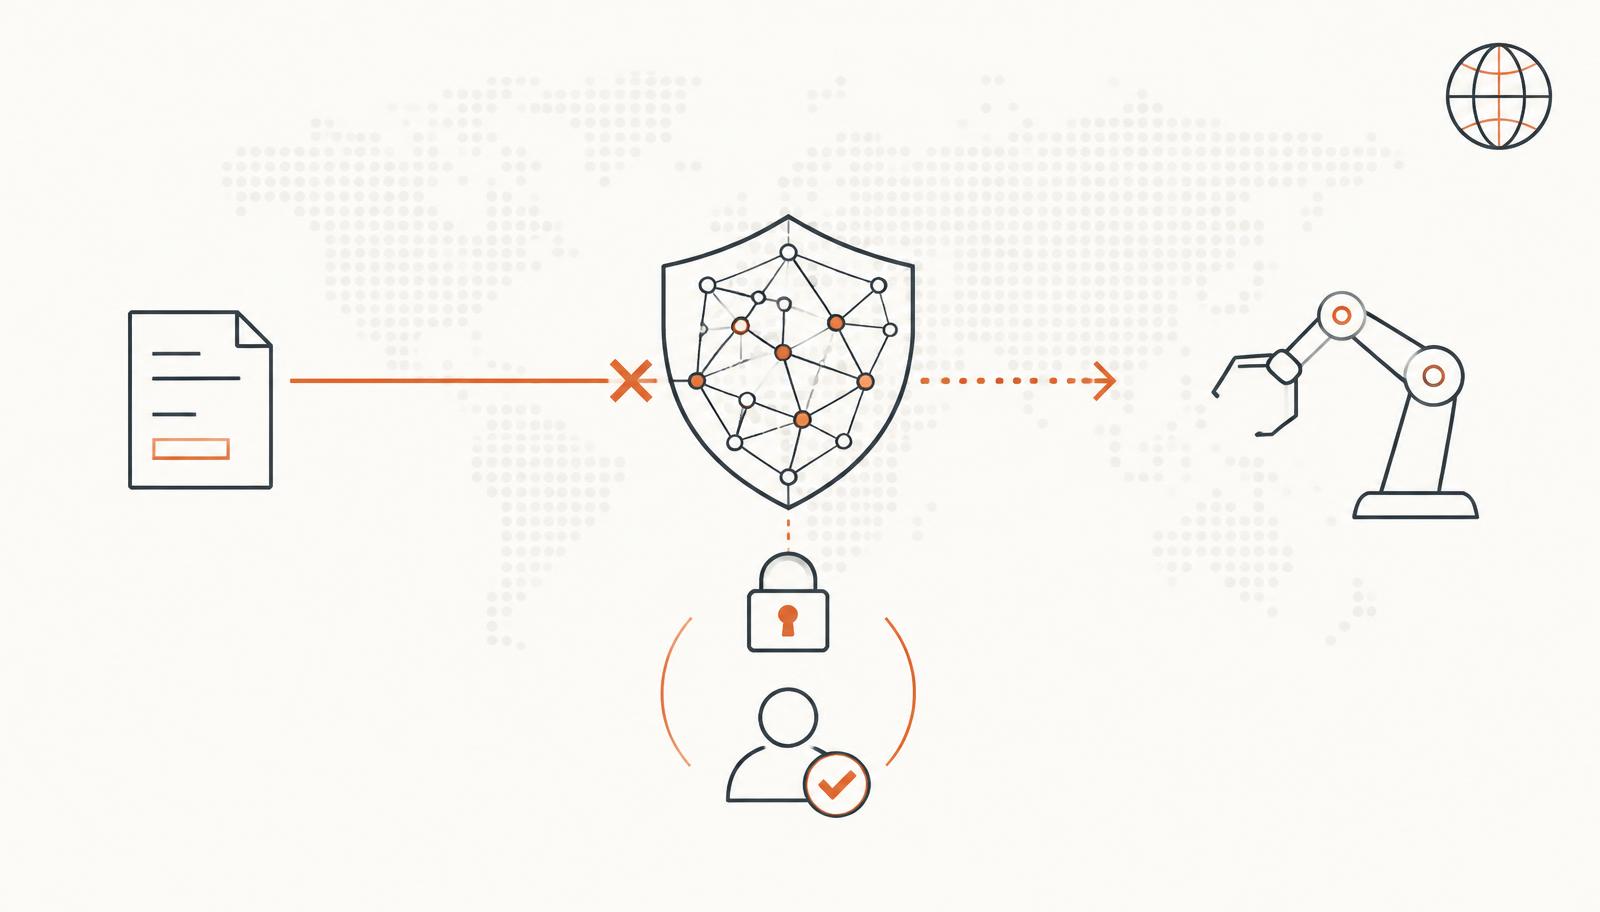
The visibility gap
Teams can explain what an agent is supposed to do while being unable to show everything it is allowed to do. Reading a document, sending an email and deleting a record are different authorities. Connecting them to one agent without clear boundaries turns a reasoning error into an operational risk.
OWASP’s 2025 guidance describes excessive agency in terms of excessive functionality, permissions and autonomy. Its prompt-injection guidance also describes indirect attacks carried in external content. These are documented risk categories, not a claim that every agent is compromised.
Risk example — illustrative, not a reported incident
A research agent reads an attacker-controlled page containing instructions to send internal notes elsewhere. If its integration can read sensitive documents and send messages without independent approval, it has both the information and the authority to attempt the leak. The dangerous part is not just the text it encountered; it is the access you delegated.
CTO actions
• Inventory tools and credentials per agent. Remove unused functions and scope access to the task, user and data required.
• Default to read-only access. Separate permissions for sending, writing and deleting; require meaningful human approval for consequential actions.
• Enforce authorization and destination checks in the application, outside the model. A prompt telling an agent to behave is not an access control.
• Test hostile instructions in documents, websites and tool responses. Log attempted and completed tool calls without unnecessarily retaining sensitive content; give an owner the ability to revoke access quickly.
The 10pm question
If your agent followed the wrong instruction tonight, what could it actually change — and which independent control would stop it?
Governance brief based on OWASP’s 2025 risk guidance, not a report of a new breach. Related guidance: LLM01:2025 Prompt Injection at genai.owasp.org. Least privilege limits damage; it does not guarantee that prompt injection disappears.
Source: OWASP GenAI Security Project · LLM06:2025 Excessive Agency